Stealth AES overview
Protect traffic between sources and destinations
Stealth AES encrypts traffic when its source or destination matches a configured rule. The switches use those rules to protect traffic while it travels between them, including replies returning to the source.
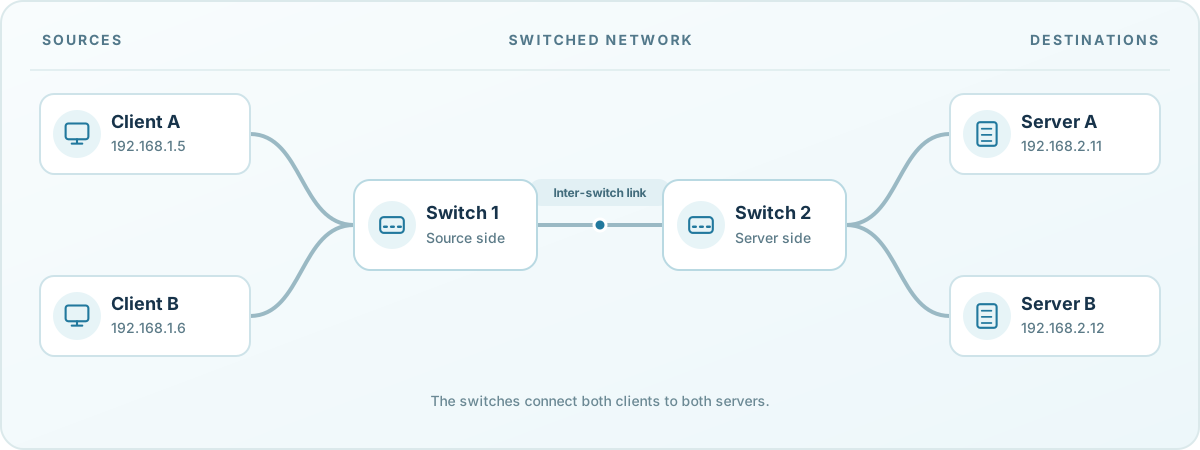
A two-switch network
Client A and Client B connect to the first switch. A second switch connects that path to Server A and Server B.
Rule in action
Encrypt traffic to and from Server A
Each switch uses configured rules to select source and destination traffic for encryption. In this example, both switches have a rule for Server A (192.168.2.11). Traffic headed to Server A is encrypted between the switches, and Server A’s replies are protected across that link in reverse.
Follow Client A’s traffic to Server A
The connection from Client A (192.168.1.5) is protocted with advanced security while in transit through the network/internet between Switch 1 and Switch 2 (192.168.2.11). None of the clients, servers or other networking devices require any special configuration or modification.
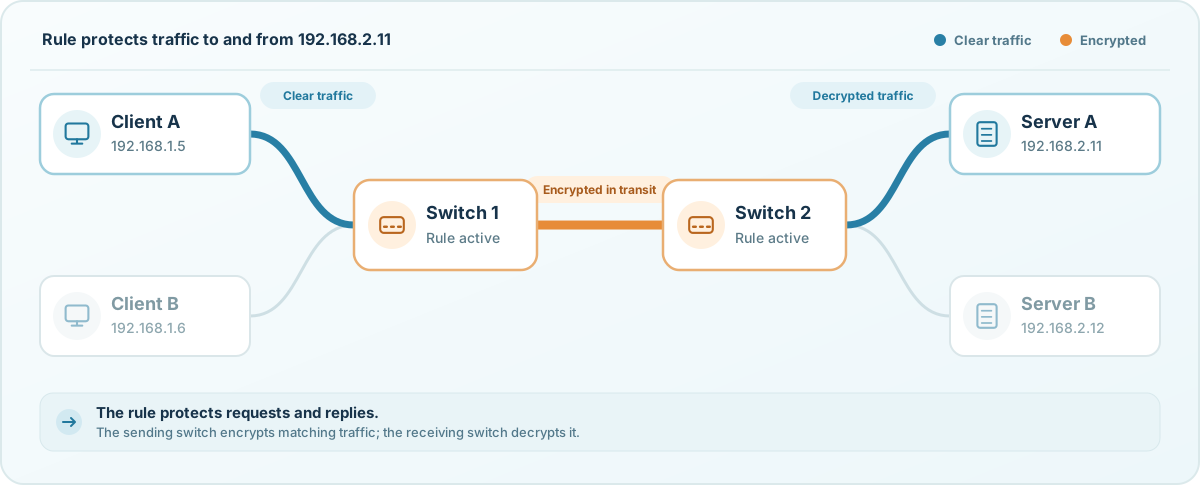
Replies from Server A follow the same path in reverse and are encrypted between the switches.